90 Day Privacy by Design Marketing Roadmap for Marketing Teams
90 Day Privacy by Design Marketing Roadmap for Marketing Teams

Privacy by design marketing means building campaigns and measurement so they collect only the data you need, by default, instead of bolting on compliance later. That approach reduces regulatory risk and, according to Google research, tends to increase customer trust and ad relevance at the same time. Tools like rdyrct, which skips IP storage entirely, show what that looks like in practice.
TL;DR:
- Building privacy into campaigns from the start reduces regulatory risk and increases customer trust, especially when default settings limit data collection and measurement.
- Marketers own the privacy experience through form design, consent management, and data minimization, making it essential to embed privacy principles throughout the campaign lifecycle.
- Privacy by design principles include obtaining explicit consent, limiting data to only what is necessary, and setting clear data retention rules to prevent over-collection and indefinite storage.
- Using privacy-enhancing tools like cookieless analytics and privacy-respecting short links helps maintain insights while respecting user privacy and reducing data exposure.
- Ongoing vendor audits, purpose-specific consent records, and lifecycle monitoring are critical to maintaining compliance and adapting to evolving regulations.
Table of Contents
- Overview: DPbDD and the marketer’s role
- The 7 principles of Privacy by Design, reframed for marketing
- Embedding privacy by design across the marketing lifecycle
- Getting consent and other legal essentials right
- Privacy tech and PETs: where they help and where they mislead
- A 90-day roadmap for privacy-first marketing teams
- Challenges and common pitfalls when implementing privacy by design
- What privacy-first marketing campaigns look like in practice
- Balancing personalization and privacy in marketing
- Tools and technologies beyond consent management platforms
- How privacy by design changes analytics and customer insight
- Where privacy regulation and marketing practice are heading
- Rdyrct: privacy-first link management built for marketers
- Why marketing leadership has to own the privacy experience
- Sources
- FAQ
Overview: DPbDD and the marketer’s role
Data Protection by Design and by Default, the legal shorthand is DPbDD, comes from GDPR Article 25, which requires organizations to build privacy protections into processing before it starts and to keep defaults set to the minimum necessary. Marketers often assume this is a legal or IT problem. It isn’t: marketing teams choose the MarTech, design the forms, and decide what gets tracked, so they own the actual privacy experience a customer has.
There’s a commercial case for taking this seriously beyond avoiding fines. Google’s Three Ms framework, Meaningful, Memorable, and Manageable, found that people who feel in control of their data are twice as likely to find advertising relevant, and are more likely to trust brands that are transparent about data use.
That gives marketers three reasons to act:
- Regulatory exposure drops when data collection matches a documented purpose.
- Trust and perceived ad relevance improve when people feel in control of their information.
- Vendor and procurement reviews move faster when privacy is already built into your stack.
The 7 principles of Privacy by Design, reframed for marketing
The original seven principles were written for systems architects, but each one has a direct marketing translation.
- Proactive, not reactive: build consent and minimization into campaign briefs before launch, not as a fix after a complaint.
- Privacy as the default: personalization and non-essential cookies stay off until a person opts in, and forms ask for the minimum fields needed.
- Full functionality, positive-sum: choose measurement that respects privacy without gutting campaign insight, such as aggregate reporting instead of individual-level tracking.
- End-to-end security: apply the same access controls and encryption to marketing data as any other customer data, including exports to agencies.
- Visibility and transparency: write plain-language notices at the point of collection, not buried in a long policy.
- Respect for user privacy: make withdrawing consent or updating preferences as easy as giving it in the first place.
- Lifecycle protection: set retention limits so campaign data doesn’t outlive its purpose, from lead capture through to CRM archiving.
Across channels, this plays out differently: email needs a visible unsubscribe and purpose-specific opt-ins, CRM needs field-level minimization, paid ads need consent-gated pixels, and landing pages need short forms with no pre-checked boxes.
Pro Tip: Start with “privacy as the default” and “visibility and transparency” first: they’re the fastest to implement and the ones auditors check first.
Embedding privacy by design across the marketing lifecycle
Treat privacy like a stage-gate, not a one-time audit. Each phase of a campaign has its own checklist.
- Planning: map what data you actually need for the campaign’s purpose, flag anything that would trigger a Data Protection Impact Assessment under high-risk processing, and cut fields that don’t serve a stated goal.
- Execution: build a consent interface that separates purposes instead of bundling them, weigh server-side tagging against client-side scripts for exposure, and prefer cookieless analytics setups where they meet your needs. Rdyrct’s cookieless analytics guide walks through this tradeoff for marketing teams.
- Measurement: report on aggregate or pseudonymous metrics, avoid fingerprinting techniques that reconstruct identity from device signals, and apply retention windows to raw event data.
- Governance: audit vendors for how they handle exports and defaults, keep consent records that show what a person agreed to and when, and require a privacy sign-off before a campaign goes live. Rdyrct’s data minimization guide covers this in more detail for marketing operations.
| Lifecycle stage | Primary action | Risk if skipped |
|---|---|---|
| Planning | Purpose mapping and data minimization | Collecting fields with no lawful basis |
| Execution | Granular consent UI, server-side tracking | Invalid consent, exposed client-side data |
| Measurement | Aggregate/pseudonymous KPIs, retention limits | Re-identification, indefinite data storage |
| Governance | Vendor audits, consent records, sign-off gates | Untracked vendor exports, audit failures |
Getting consent and other legal essentials right
Valid consent under most privacy frameworks has to be freely given, specific, informed, unambiguous, and just as easy to withdraw as it was to give. Regulatory guidance on consent standards consistently flags cookie walls and bundled consent, where accepting one purpose forces acceptance of all others, as invalid patterns that regulators scrutinize closely.
Common red flags to avoid:
- A single “accept all” button with no way to select individual purposes.
- Consent buried inside a long privacy policy instead of shown at the point of collection.
- No visible or equally easy way to withdraw consent later.
- Treating silence or continued browsing as consent.
Keep separate consent records for each purpose, marketing emails, ad personalization, analytics, so a person can withdraw from one without losing the others. When a use case doesn’t fit consent cleanly, such as basic fraud prevention or contractual necessity, loop in legal early to confirm an alternative lawful basis rather than defaulting to consent as a catch-all.
Privacy tech and PETs: where they help and where they mislead
Privacy-enhancing technologies (PETs), including data clean rooms and server-side tracking, can reduce how much raw personal data flows between systems. Cookieless analytics setups fall into this category too. But FTC guidance on data clean rooms makes clear these tools don’t automatically confer compliance: misconfiguration or permissive vendor defaults can still expose data, even inside a system marketed as privacy-safe.
Treat PETs as tools, not legal shields. They don’t remove your obligation to establish a lawful basis for processing in the first place.
Operational guardrails worth setting:
- Vet vendors on their default export settings, not just their marketing claims.
- Monitor what data actually leaves a clean room or measurement platform, not just what’s configured to leave it.
- Reduce the surface area of what you collect before reaching for a PET to protect it.
Pro Tip: Ask any vendor what happens by default, not what’s possible if you configure it correctly.
A 90-day roadmap for privacy-first marketing teams
Rolling this out works better as sprints than as a single overhaul.
- Days 1 to 30: map current data collection against actual purposes, fix quick UI wins like pre-checked consent boxes, and build a vendor checklist covering default export behavior.
- Days 31 to 60: shift measurement toward cookieless or aggregate methods, run a small experiment comparing a privacy-forward experience to your current one, and automate retention rules for stale campaign data.
- Days 61 to 90: formalize governance with sign-off gates, complete a DPIA for any high-risk processing identified in month one, and test brand lift between privacy-forward and control experiences.
Track a small set of metrics throughout: consent rate by purpose, any shift in brand trust measures, and changes in ad relevance scores. Google’s testing found that people who feel in control of their data are twice as likely to find advertising relevant, which makes consent rate and relevance worth tracking together rather than in isolation.
Challenges and common pitfalls when implementing privacy by design
The most common failure isn’t a lack of intent, it’s treating privacy as a one-time project instead of an ongoing default. Teams write a policy, update a cookie banner, and consider the work done, while new campaigns and new vendors quietly reintroduce the same over-collection habits.
Cross-team friction is another recurring problem. Legal wants strict minimization, growth teams want richer targeting data, and without a shared checklist those two goals collide on every launch. The FTC’s staff report on surveillance practices points to exactly this pattern at scale: mass data collection that outpaced any stated purpose, often because no one owned the decision to stop collecting.
Vendor sprawl compounds the issue. Every new pixel, tag, or integration adds a data path that someone has to audit, and most teams don’t revisit old vendor contracts once they’re live. Retention is the quiet failure point too: campaigns end, but the data they generated often sits untouched for years with no clear reason.
The fix isn’t more policy documents. It’s a repeatable checklist applied at every campaign launch, the kind covered in the lifecycle section above, so privacy defaults survive team turnover and new tool adoption instead of eroding one campaign at a time.
What privacy-first marketing campaigns look like in practice
Successful privacy-by-design campaigns share a common thread: they shrink the data footprint without shrinking the insight. A campaign reporting click-through by country and device type, without ever storing an individual’s IP address, still tells a marketing team where to invest, just without the liability of holding data it never needed.
Short link and QR code campaigns are a practical example. A branded QR code on packaging or a print ad can report referrer, device type, and country-level clicks, giving a team real campaign performance data without collecting anything that identifies an individual visitor. Rdyrct’s country-level click analytics approach reflects this: revenue-relevant signal, not personal identifiers.
Email campaigns that separate consent by purpose, newsletter versus promotional offers versus product updates, tend to see fewer complaints and cleaner unsubscribe data, because people opted into exactly what they’re receiving rather than a blanket subscription. That granularity, covered under the EDPB’s consent guidance, also makes audits faster because each consent record maps to one clear purpose.
The pattern across these examples is consistency: privacy-forward campaigns still answer the marketing question, which channel worked, which audience responded, without keeping data that was never load-bearing for that answer.
Balancing personalization and privacy in marketing
Personalization and privacy aren’t opposites, but they do require trade-offs most teams never explicitly make. The instinct is to collect everything possible in case it’s useful later. The privacy-by-design instinct is to ask what personalization actually needs and stop there.
Segment-level personalization, tailoring by broad interest category or geography, delivers most of the relevance benefit without needing individual-level tracking. Reserve granular, identity-based personalization for contexts where a person has explicitly opted in, such as a logged-in account experience, rather than applying it silently across anonymous site visitors.
Aggregate and cohort-based targeting is another middle path: it lets a team optimize creative and timing based on group behavior instead of individual profiles. This is where the Three Ms framework matters most: Google’s research found that when people feel in control of their data, they respond better to the same targeted content, not worse. Control, not the absence of personalization, is what drives the trust gain.

The practical rule is to default to the least invasive form of personalization that still meets the campaign goal, and treat any request for more granular data as something that needs its own explicit justification and consent flow, not an assumption baked into the tool from day one.
Tools and technologies beyond consent management platforms
Consent management platforms get most of the attention, but they’re only one piece of a privacy-by-design stack. Server-side tagging routes data through a controlled server before it reaches third-party tools, reducing what client-side scripts can see or leak. Cookieless analytics, covered in rdyrct’s guide to measuring without third-party cookies, replace persistent identifiers with aggregate or session-based measurement.
Privacy-respecting link management is a less obvious but practical tool. A short link platform that skips IP storage, like rdyrct, lets marketers track referrer, device, and country-level performance on campaigns without the underlying risk of holding identifiable location data. Custom domain short links, detailed in rdyrct’s setup guide, also give brands a trust signal, since a branded domain looks less like a generic tracking redirect.
Data clean rooms, discussed by the FTC, let two parties analyze combined data without either side seeing the other’s raw records, useful for co-marketing or media partnerships. For technical implementation support, a digital agency experienced in privacy-first UX and consent flows can help translate these choices into actual site behavior, and hosting or build partners like BasicBS matter too, since where data is processed and stored affects your compliance posture as much as what you collect.

How privacy by design changes analytics and customer insight
Moving to privacy-first measurement does change what a marketing team can see, but the change is narrower than most people expect. You lose individual-level journey stitching across devices and sessions when identifiers disappear. What you keep, often at similar quality, is aggregate performance: which campaigns drove clicks, which channels converted, which geographies responded.
The ICO’s guidance on data protection by design frames this as a practical tradeoff rather than a loss: mapping, minimization, and access controls reduce the risk of a costly re-architecture later, and often speed up procurement in regulated sectors where privacy certifications get evaluated during vendor selection.
Pseudonymization at the point of data collection is one of the more effective practical shifts here. Rather than stripping data of value after the fact, marketing teams can pseudonymize data at ingestion, avoid storing raw IP addresses, and apply automatic retention rules, which also reduces the burden of responding to data subject access requests later. The insight a team loses tends to be the kind that was never load-bearing anyway: knowing exactly which individual clicked a link rarely changes a campaign decision the way knowing which segment or channel performed does.
Where privacy regulation and marketing practice are heading
Regulatory attention on marketing data practices is not slowing down. The FTC’s 2024 staff report recommended baseline protections including data minimization and clearer retention policies, signaling that enforcement priorities are shifting toward how long data is kept, not just how it’s collected.
Expect continued scrutiny of pixels and tracking-based ad models, alongside growing expectations that PETs like data clean rooms come with documented governance rather than being treated as a compliance shortcut. The EDPB’s Article 25 guidelines already require DPbDD to be built in from the start of processing, and that expectation is likely to extend into more marketing-specific enforcement as regulators catch up with ad tech practices.
For marketing teams, the direction is consistent even if specific rules vary by market: less reliance on individual-level tracking, more emphasis on documented purpose and retention limits, and closer alignment between what a privacy notice says and what the MarTech stack actually does. Teams that build minimization and transparency into their process now will have less to unwind later, regardless of which specific regulation lands next.
Rdyrct: privacy-first link management built for marketers
Rdyrct turns long URLs into branded short links with a UTM builder, branded QR codes, and privacy-respecting analytics that report country, referrer, and device data without ever storing IP addresses.
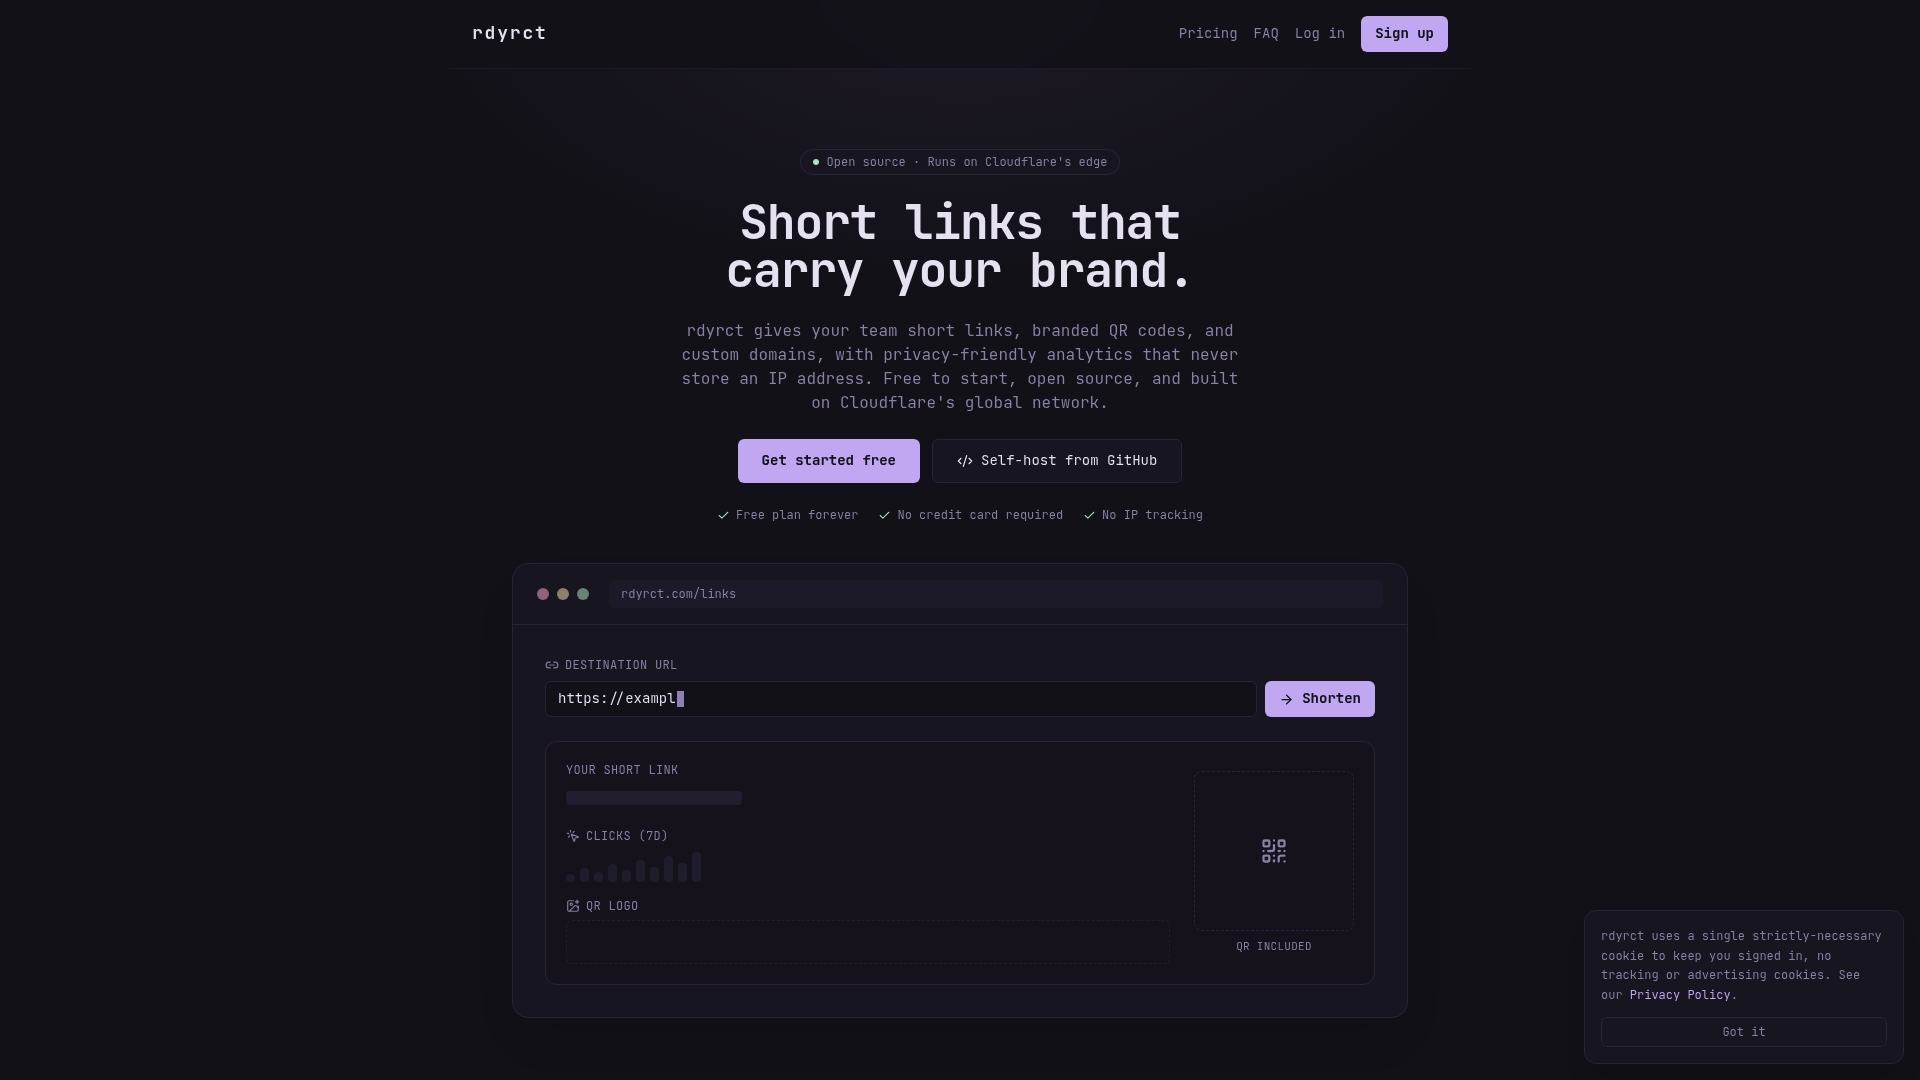
That structure maps directly onto the lifecycle checklist above: minimization by default, no individual-level tracking to govern, and cookieless-friendly reporting out of the box. Plans run from a free tier through paid plans that unlock branded QR codes, custom domains, and longer analytics history. Check the pricing page to compare tiers against your campaign volume.
Why marketing leadership has to own the privacy experience
Legal can write the policy, but marketing designs the form, picks the pixel, and decides what gets asked at signup. When I’ve seen a team default a signup field to unchecked instead of pre-checked, conversion barely moved and trust signals did. Read more on rdyrct’s blog.
— Andrea
Sources
- Privacy in modern marketing — Google / Think with Google
- Guidelines 4/2019 on Article 25 Data protection by design and by default — EDPB
- Data clean rooms: separating fact from fiction — FTC (2024-11-13)
- Data protection by design and by default — ICO
FAQ
What are the 7 principles of privacy by design?
The seven principles are proactive rather than reactive protection, privacy as the default setting, privacy embedded into design, full functionality in a positive-sum way, end-to-end security, visibility and transparency, and respect for user privacy. In marketing, these translate into practices like minimal forms, opt-in personalization, and clear consent notices at the point of collection.
What is a privacy by design approach?
A privacy by design approach means building data protection into a product, campaign, or system from the start, rather than adding compliance measures after launch. Under GDPR Article 25, this includes setting minimal data collection as the default and building in technical safeguards throughout the processing lifecycle.
What are examples of privacy by design in marketing?
Examples include forms that request only the fields a campaign actually needs, analytics that report aggregate metrics like country or device type instead of individual identifiers, and consent flows that let a person opt into email marketing without also agreeing to ad personalization. Short link tools that skip IP storage, such as rdyrct, are another practical example.
What is GDPR vs CCPA?
GDPR is the European Union’s data protection law requiring lawful basis for processing and Data Protection by Design and by Default under Article 25, while CCPA is a California law focused on consumer rights to know, delete, and opt out of the sale of personal information. They share goals around transparency and control but differ in scope, enforcement mechanisms, and specific requirements, so marketers operating across regions need to check which rules apply to each audience.
How do marketers implement privacy by design practically?
Marketers start by mapping what data a campaign actually needs, setting non-essential tracking to off by default, and building consent flows that separate purposes instead of bundling them. Ongoing steps include auditing vendors for default export settings, applying retention limits to campaign data, and using measurement tools that report aggregate insight rather than individual-level tracking.